When you run a mapping with an Access Policy transformation, you can audit the rules that the transformation applies to your data and audit the columns or rows that the rules apply to. Find the audit information in the session log, You can download the session log from the My Jobs page.
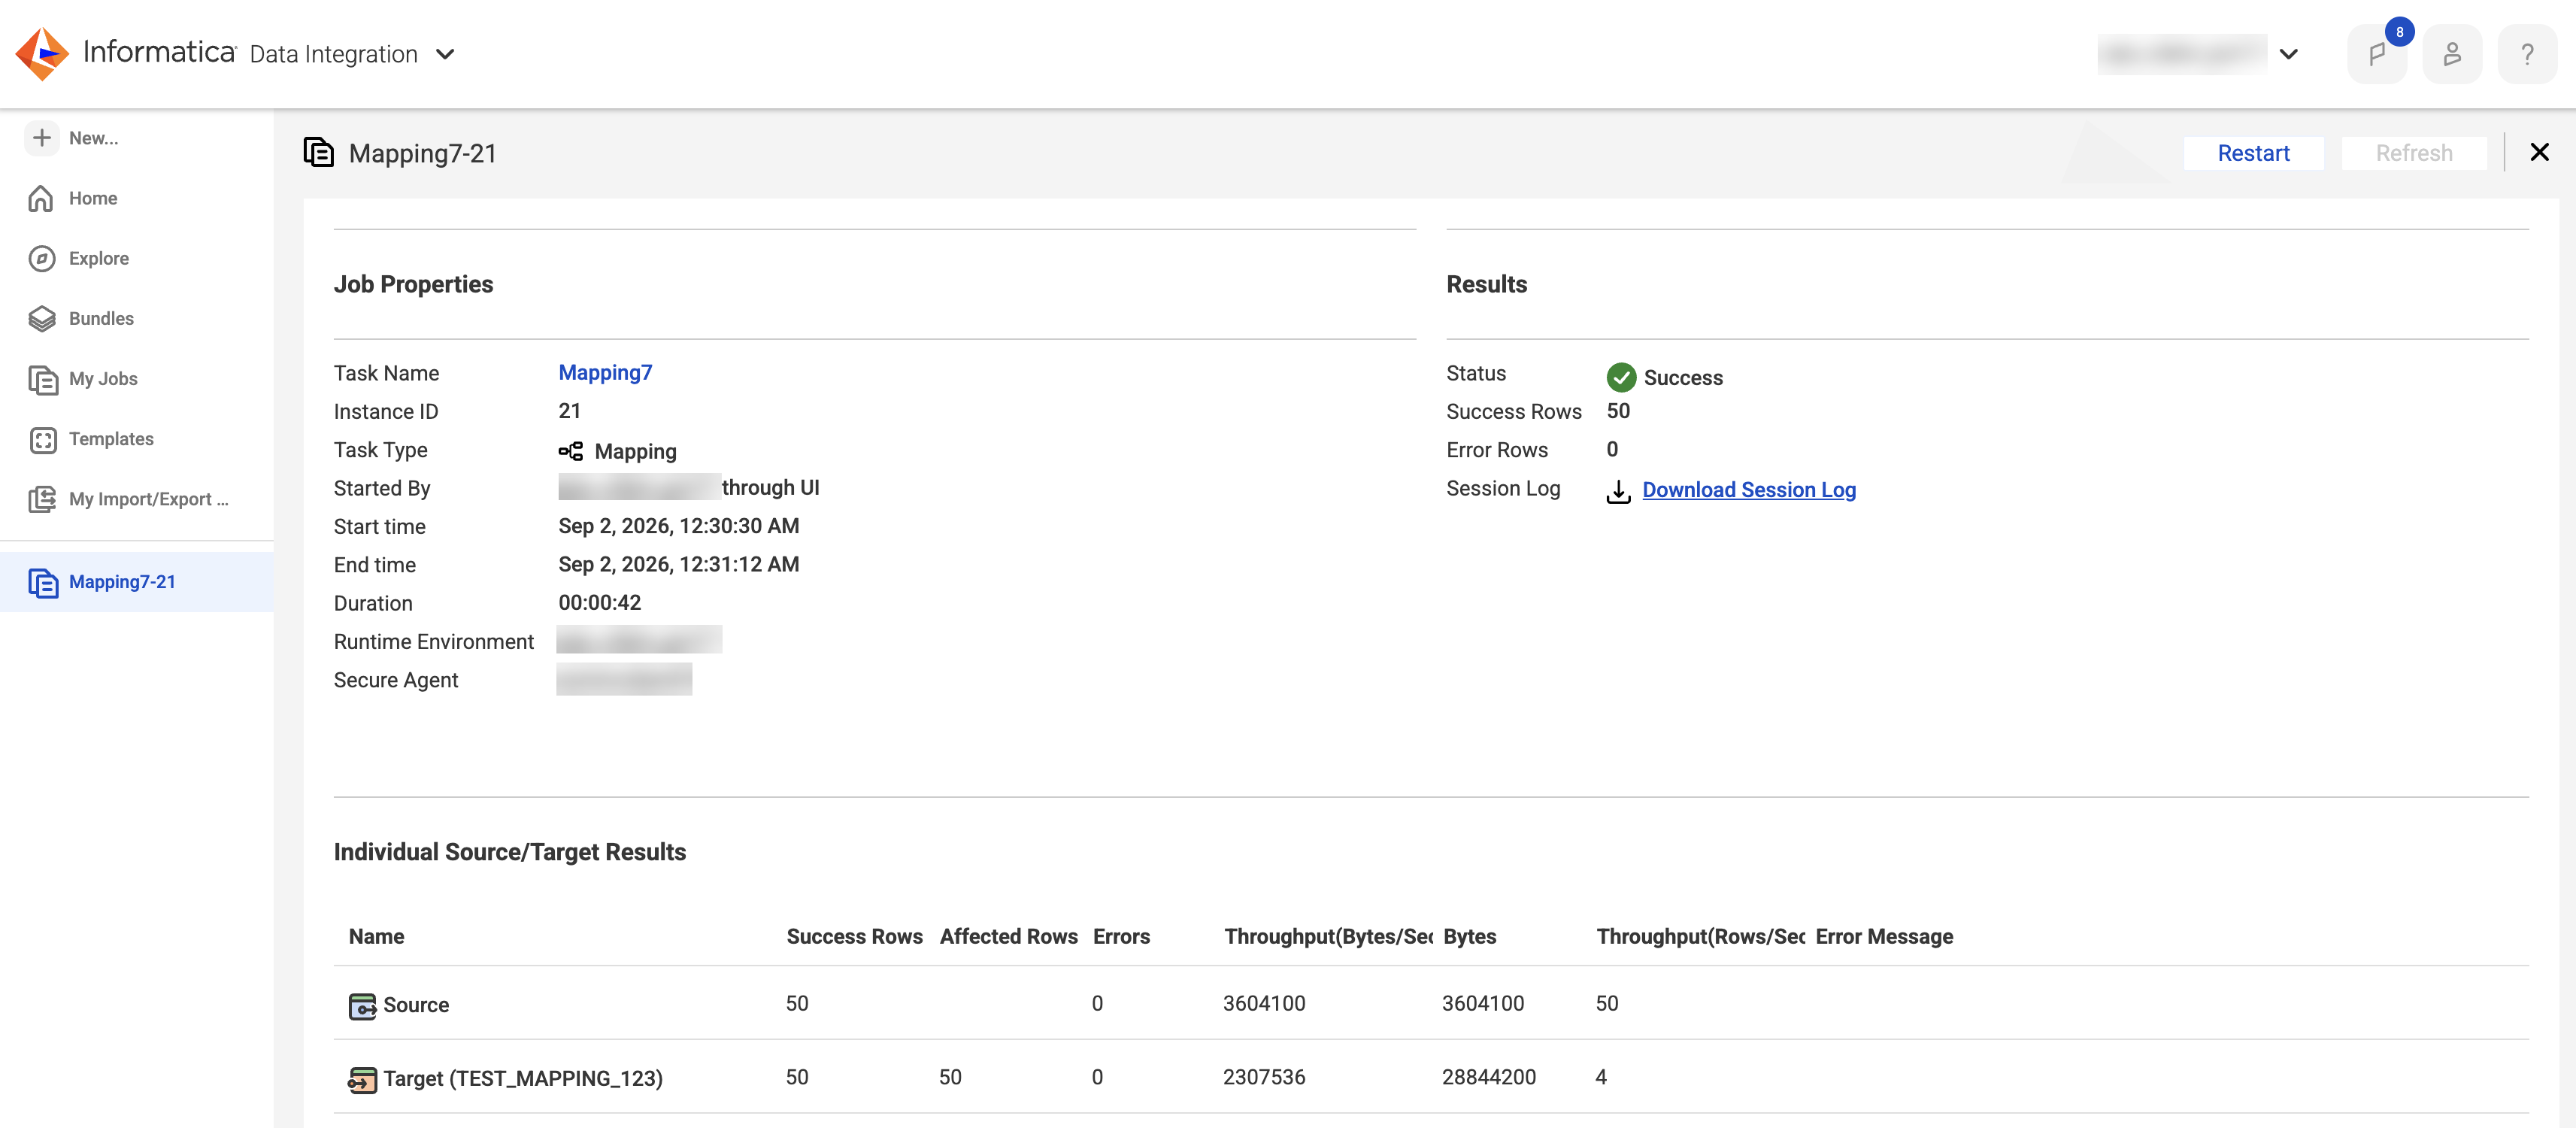
The following image shows the job properties of a mapping with a link to download the session log:
After you select an instance of the mapping execution, you can download the session log. The session log displays the rules applied and the columns or rows that the rules were applied to.
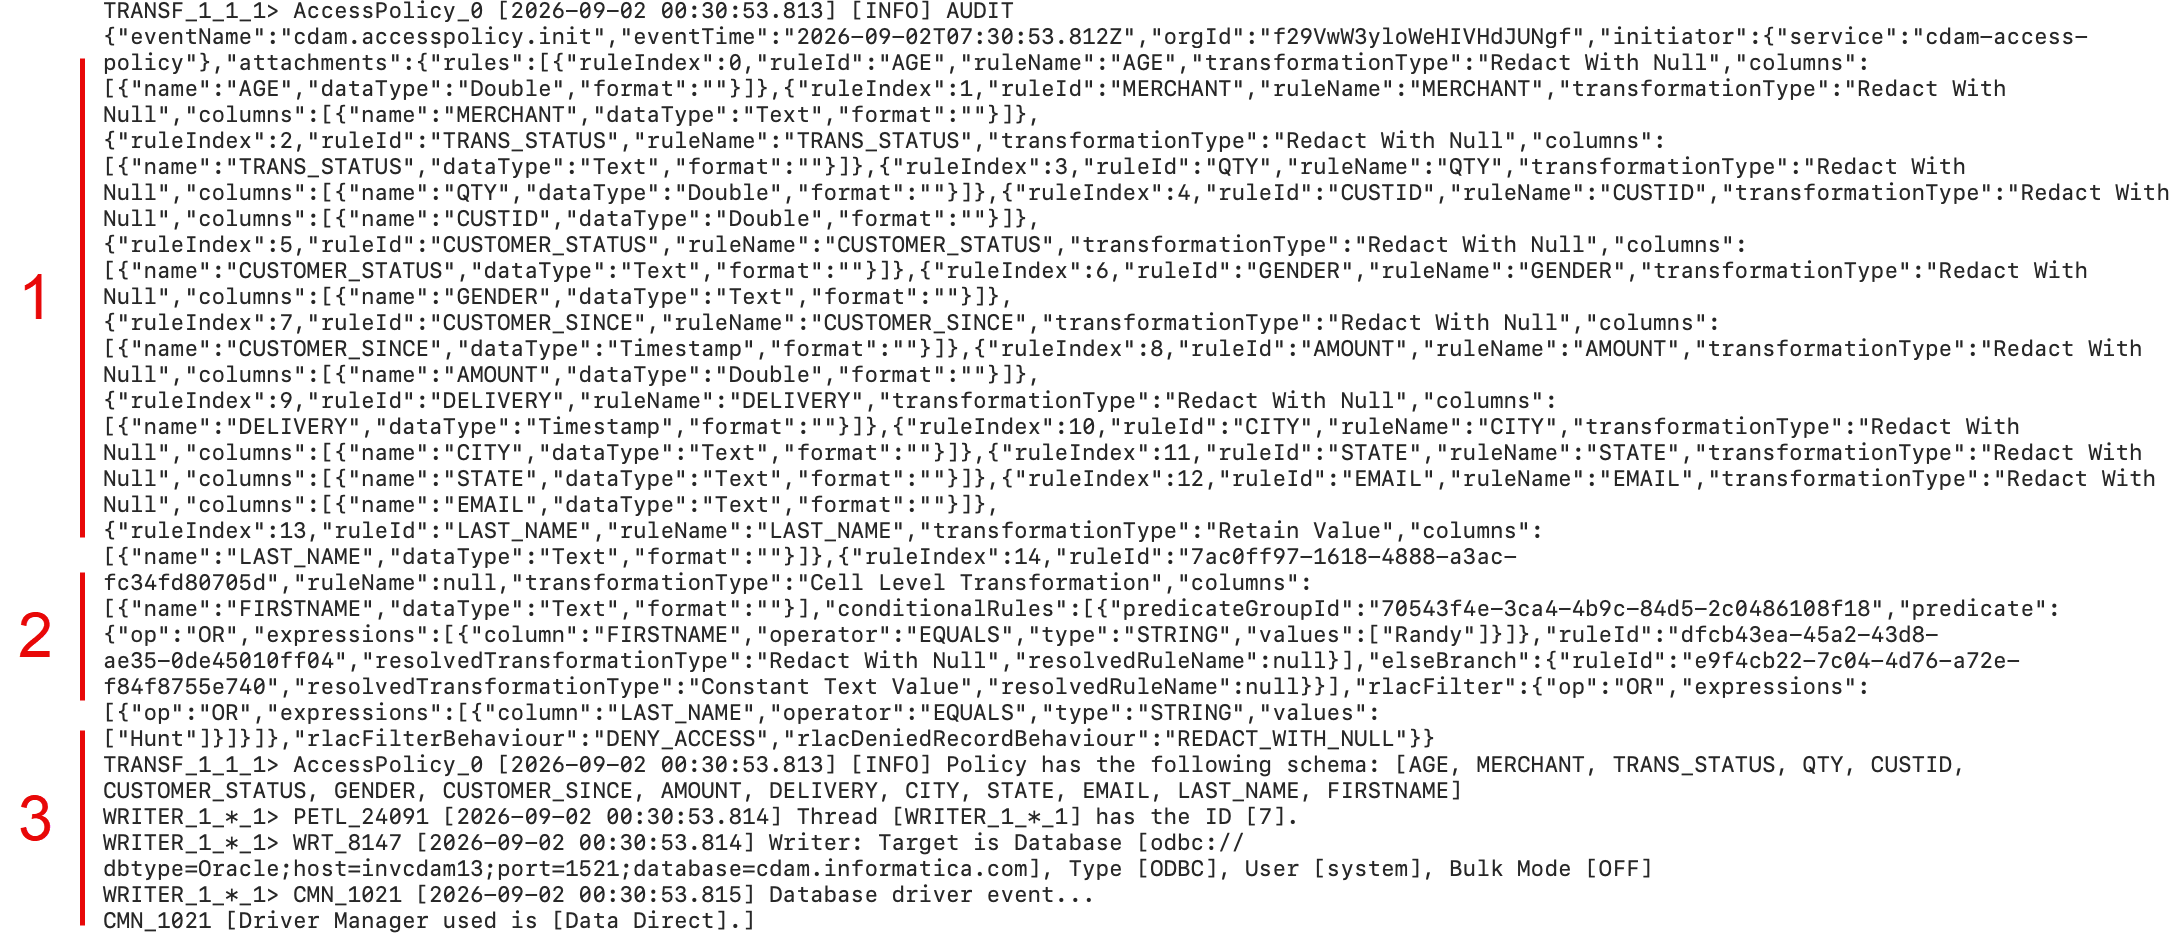
The following image shows a session log:
The log includes information about the following types of rule conditions that the transformation applies to the data:
1Field-level conditions of a data de-identification rule
2Cell-level conditions of a data de-identification rule