Configure privileges for user roles in Business 360 Console
You can configure privileges and create data access rules for custom user roles on the Security page of Business 360 Console.
The User Roles tab on the Security page lists all the custom user roles that you create in Administrator. You can select the custom user roles to configure privileges. The Data Access Rules tab on the Security page lists the existing data access rules for custom user roles. For more information about data access rules, see Managing data access rules.
Note:
Any changes that you make to roles and their privileges in the Administrator module are effective after an hour of synchronization.
You can configure permissions for user roles to access dynamic field definitions and dynamic field values attributes, but not for specific fields and field groups in dynamic pools.
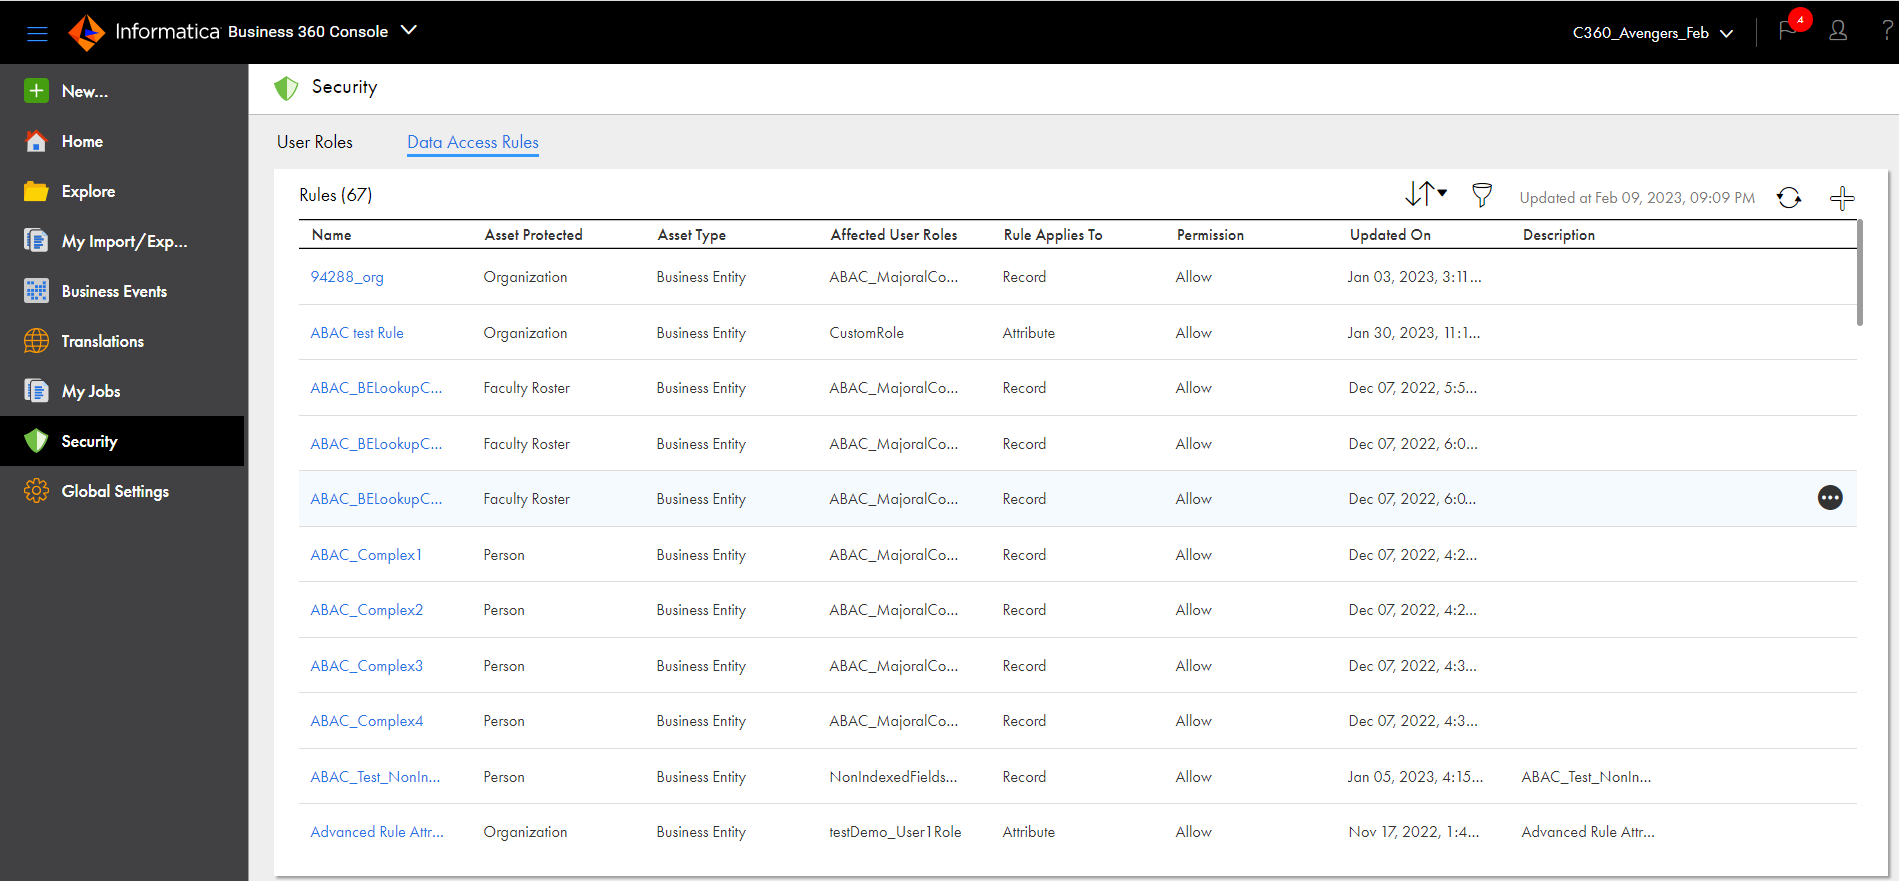
The following image shows the list of data access rules on the Security page:
You can use filters to find specific data access rules. To filter data access rules, click the Filter icon. To specify a filter, click Add Field, and select the property to filter by.
Note:
To ensure that you view the list of up-to-date custom user roles and data access rules, refresh the Security page.
After you assign privileges on the Security page, don't rename the custom user role in Administrator. If you rename the custom user role, the following errors occur:
•The existing privileges on the Records tab of business entities, relationships, and hierarchies are cleared.
•The workflow privileges assigned on the Features tab are cleared.
•The asset-level privileges for business entities assigned for the custom user role in Administrator override the existing privileges on the Metadata tab of the business entity.
Configure privileges for a business entity
You can configure privileges related to a single business entity or multiple business entities for a custom user role. The configured privileges are your basis to configure data access rules for selected business entities.
Ensure you configure appropriate base privileges for the business entities to all the roles that you intend to configure data access rules.
1In Business 360 Console, on the Security page, click the custom user role for which you want to configure privileges.
The user role details page appears and lists the business entities for which the user role has access permissions. The following image shows the user role details page:
2Select the business entity for which you want to configure privileges.
3 On the following tabs, select required permissions:
- Records. Lists privileges that allow users to create, read, update, delete, and unmerge records in the business applications. You can specify whether users can perform tasks that triggers jobs. You can also specify whether users can access some components in the business applications. For more information, see Configure privileges for business application user roles.
You can configure privileges related to a single relationship or multiple relationships for a custom user role.
Assign required permission for relationships on the Assets tab of the MDM Configuration service in Administrator for a custom user role.
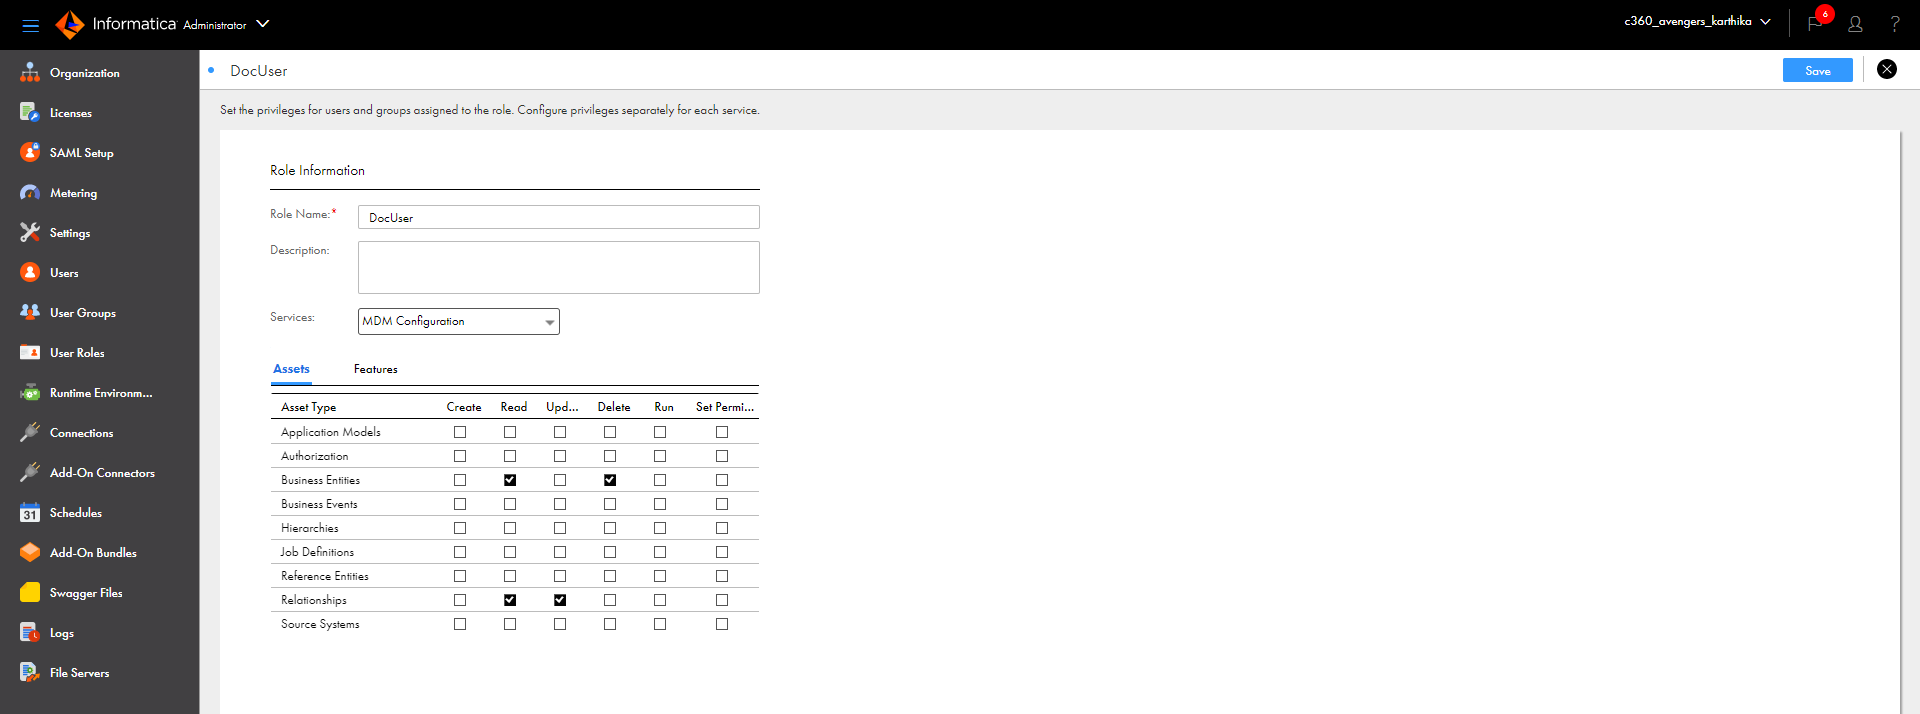
The following image shows the user role details page in Administrator with relationship privileges assigned for a custom user role:
1In Business 360 Console, on the Security page, click the custom user role for which you want to configure privileges.
The user role details page appears.
2On the Relationship tab, select the relationship for which you want to configure privileges.
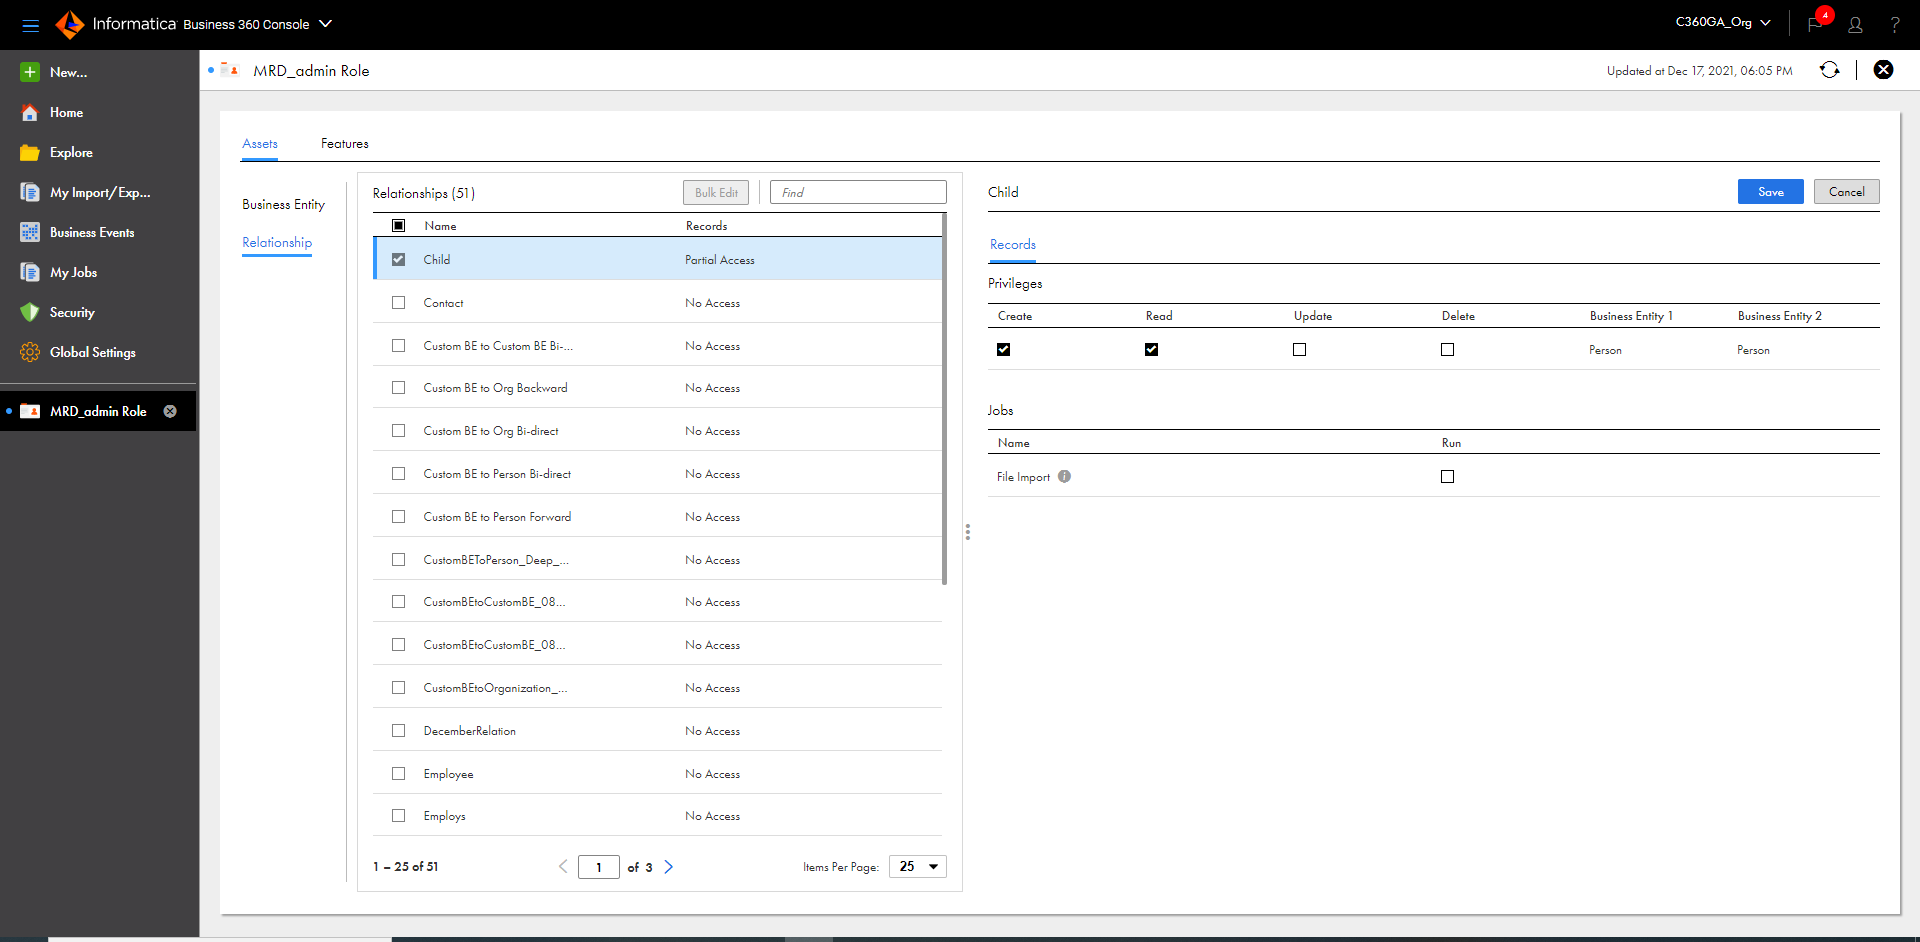
The following image shows the Relationship tab with the list of predefined and custom relationships:
3On the Records tab, select create, read, update, and delete privileges pertaining to related records in the business applications. You can also specify whether users can import relationship data. For more information, see Configure related records privileges for business application users.
Configure privileges for a hierarchy
You can configure privileges related to hierarchies for a custom user role.
Before you assign privileges for hierarchies on the Security page, you can assign privileges for hierarchy models on the Assets tab of the MDM Configuration service in Administrator for a custom user role if required.
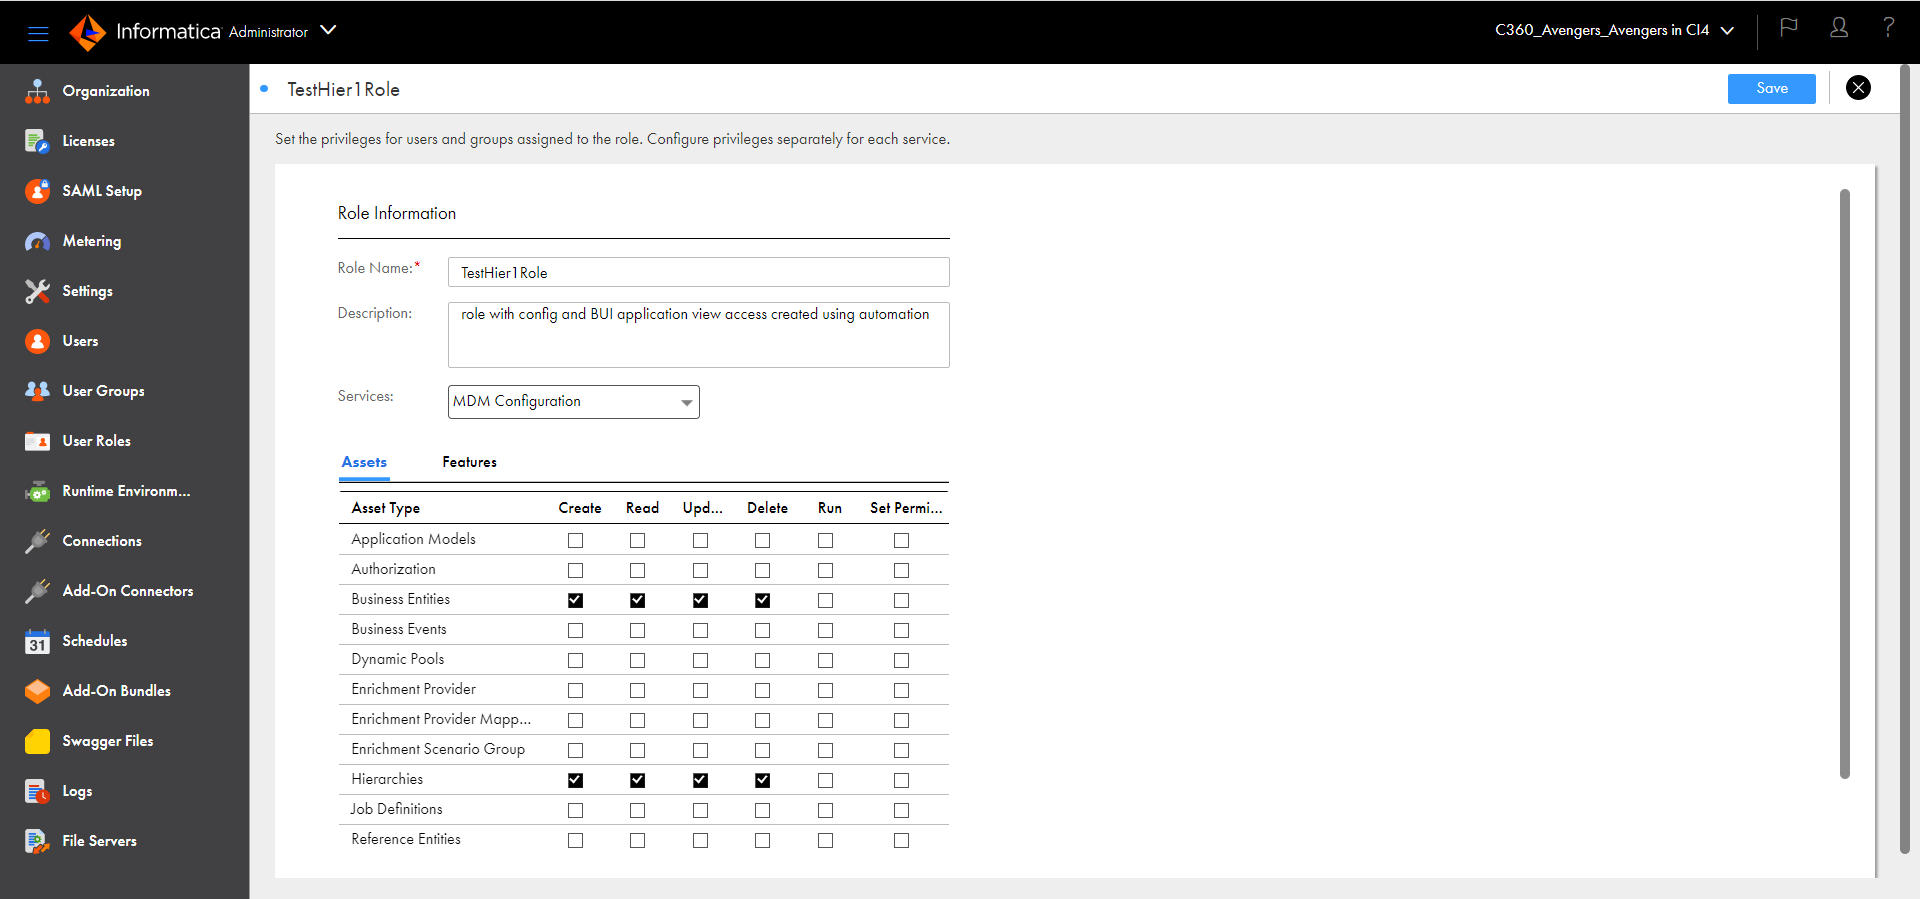
The following image shows the user role details page in Administrator with the hierarchy privileges assigned for a custom user role:
1In Business 360 Console, on the Security page, click the custom user role for which you want to configure privileges.
The user role details page appears.
2On the Assets tab, select Hierarchy from the Show: list.
The list of hierarchy models appears on the left pane.
3 Select the required hierarchy model.
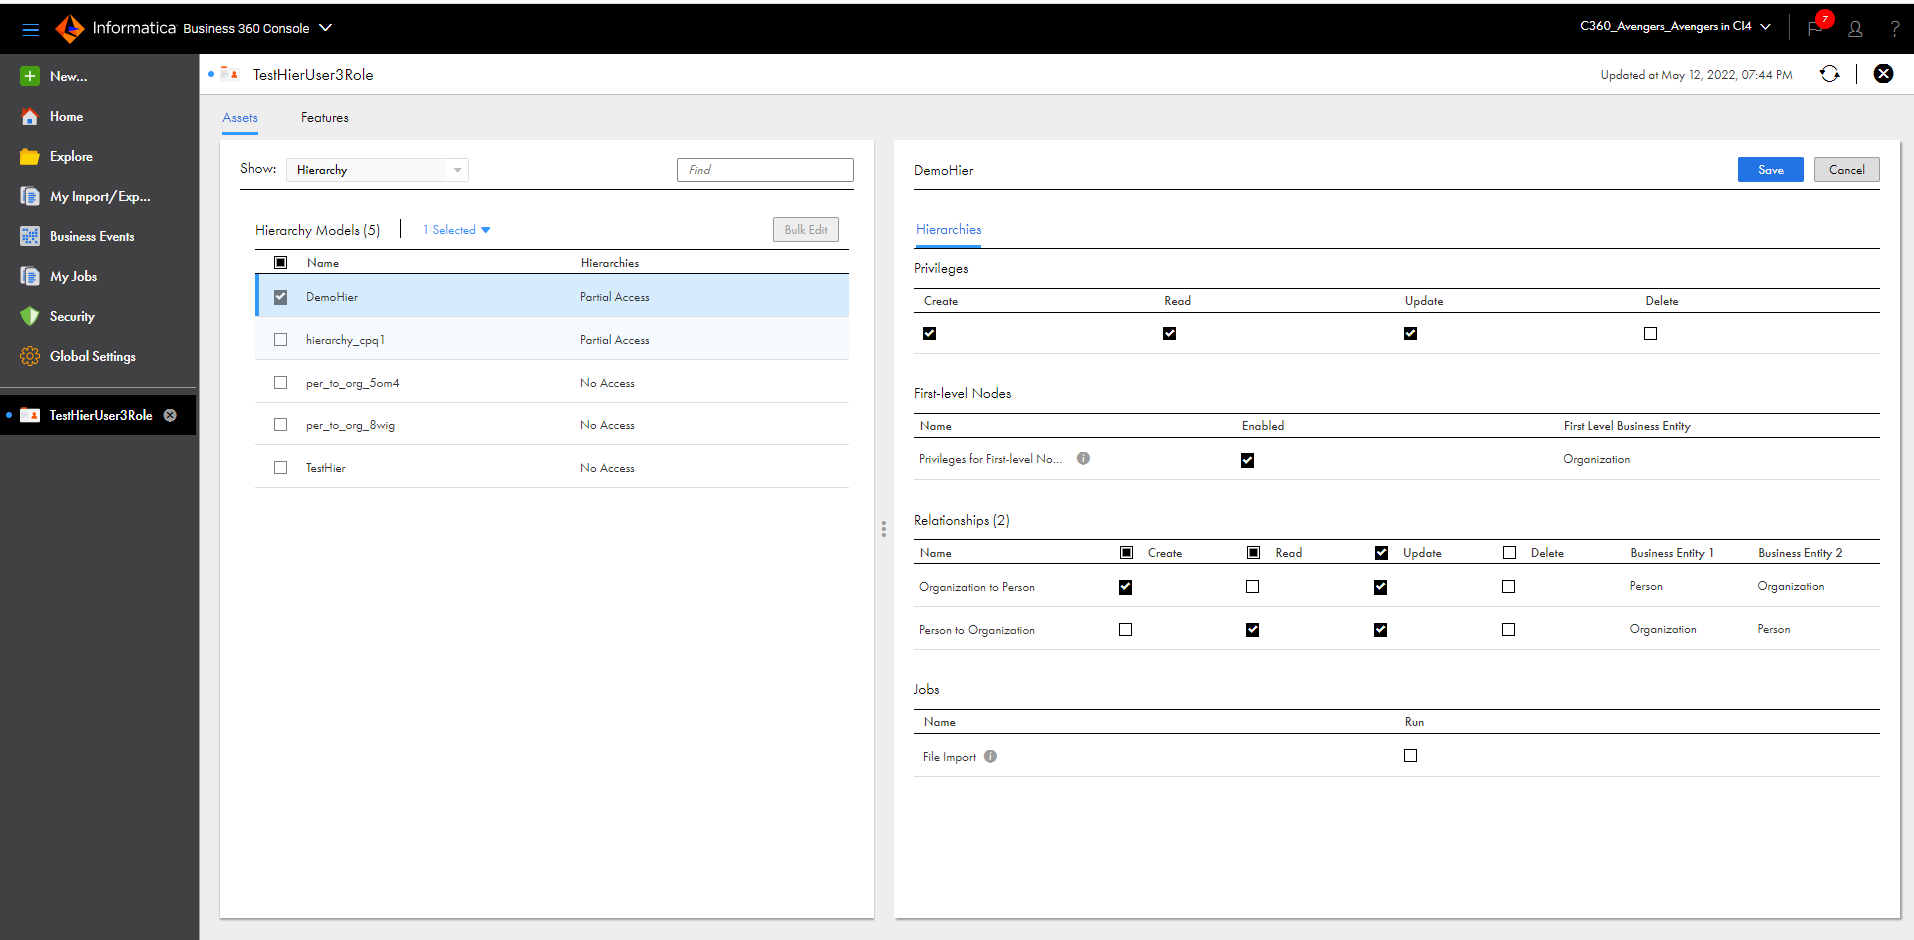
The privileges for the hierarchies based on the selected hierarchy model appear on the right pane.
The following image shows the list of hierarchy models on the left pane and the corresponding hierarchies and their privileges on the right pane:
4On the right pane, configure privileges to control access to hierarchies, first-level nodes, and relationships within hierarchies. You can also specify whether users can import hierarchy data. For more information, see Configure hierarchy privileges for business application users.
Configuring privileges for downloading match output
You can control custom user roles that can download match output reports from the match and merge job details page and export match pair details of source records in business applications. For predefined user roles, assign them a custom user role that includes the privilege to download match output reports.
1In Business 360 Console, on the Security page, click the custom user role for which you want to configure the privilege.
2On the Features tab of the user role details page, enable Download Match Output.
3Click Save.
Note:
The data in the match output report might not be based on the data access rules that are assigned to custom user roles.
For more information about configuring privileges for downloading match output reports from the match and merge job details page and exporting match pair details of source records in business applications, watch the Download Match Output video.
Configuring privileges for managing shared objects
You can enable the Manage Shared Objects privilege to allow a custom user role to edit or delete shared objects, such as dashboards, saved searches, and search templates, or change their sharing settings.
Additionally, when you enable this privilege, the user role can add or remove a dashboard from everyone's Home page in business applications.
By default, predefined user roles, such as Admin, Customer 360 Manager, Product 360 Manager, and Supplier 360 Data Steward, have this privilege enabled.
For example, consider that your organization has two custom user roles, such as Analyst and Coordinator, and the predefined user role Customer 360 Manager. If a user with the Analyst user role creates a saved search and shares it with everyone, users with the Coordinator and Customer 360 Manager user roles can access the shared saved search. They can run the shared saved search and view the records. However, only users with the Customer 360 Manager user role can rename or delete the shared saved search, or update the sharing settings of the shared saved search. If you want users with the Coordinator user role to manage the shared objects similar to a Customer 360 Manager user role, you must assign the Manage Shared Objects privilege.
1In Business 360 Console, on the Security page, click the custom user role for which you want to configure the privilege.
2On the Features tab of the user role details page, select Manage Shared Objects.
3Click Save.
Configuring privileges for training Adaptive AI match models
You can provide access to custom user roles for training Adaptive AI match models. By default, user roles don't have access to the Adaptive AI match model page within a match model configuration.
For predefined user roles, you can assign a custom user role that includes the privilege to train Adaptive AI match models.
1In Business 360 Console, on the Security page, click the custom user role for which you want to configure the privilege.
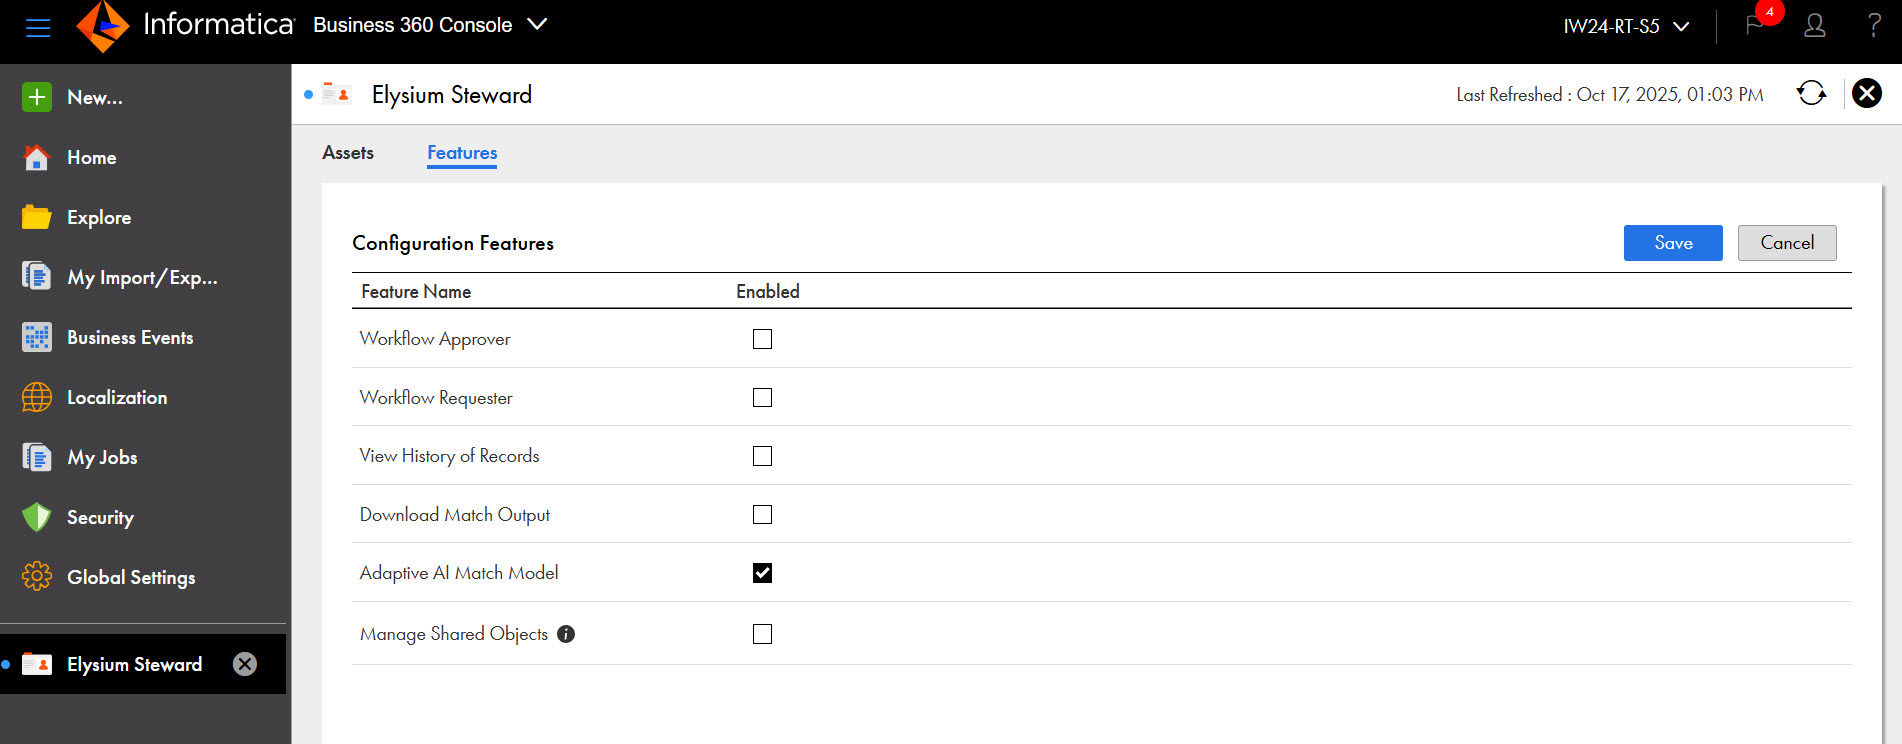
2On the Features tab of the user role details page, select Adaptive AI Match Model.
The following image shows the Adaptive AI Match Model privilege enabled for a custom user role: