Configure record privileges for business application user roles
You can configure privileges that specify whether users can create, read, update, delete, and unmerge records. You can specify whether the users can access all fields, certain fields, or none. You can also specify whether the users can import data without matching, export search results, or import or export data after matching.
Records
You can configure privileges that specify whether users can create, read, update, and delete fields within a record in your business application.
The read privileges that you assign for a user role impact the reports in the following ways:
•If a user role doesn't have the read privileges for the records in a business entity, the users can't create reports for the business entity.
•If a user role doesn't have read privileges for the attributes in a business entity, the users can create reports for the business entity. But they can't view the affected attributes when they create reports for the business entity.
•If a user role doesn't have read privileges for the records or attributes in a business entity, the users can't view reports or charts related to the business entity.
The following table describes the behaviour of record privileges:
Privileges
Set to Enabled
Create
Create business entity records.
Read
Search and view records that belong to the business entity.
Update
Update the existing field values of all records that belong to the business entity.
Note:
Ensure that you also set the read privilege. Without the read privilege, the record is not visible for the user to update it.
Delete
Delete records, field group values, and field values.
Note:
Ensure that you also set the read privilege. Without the read privilege, the record is not visible for the user to delete it.
Merge
Merge source and master records.
Unmerge
Unmerge source records.
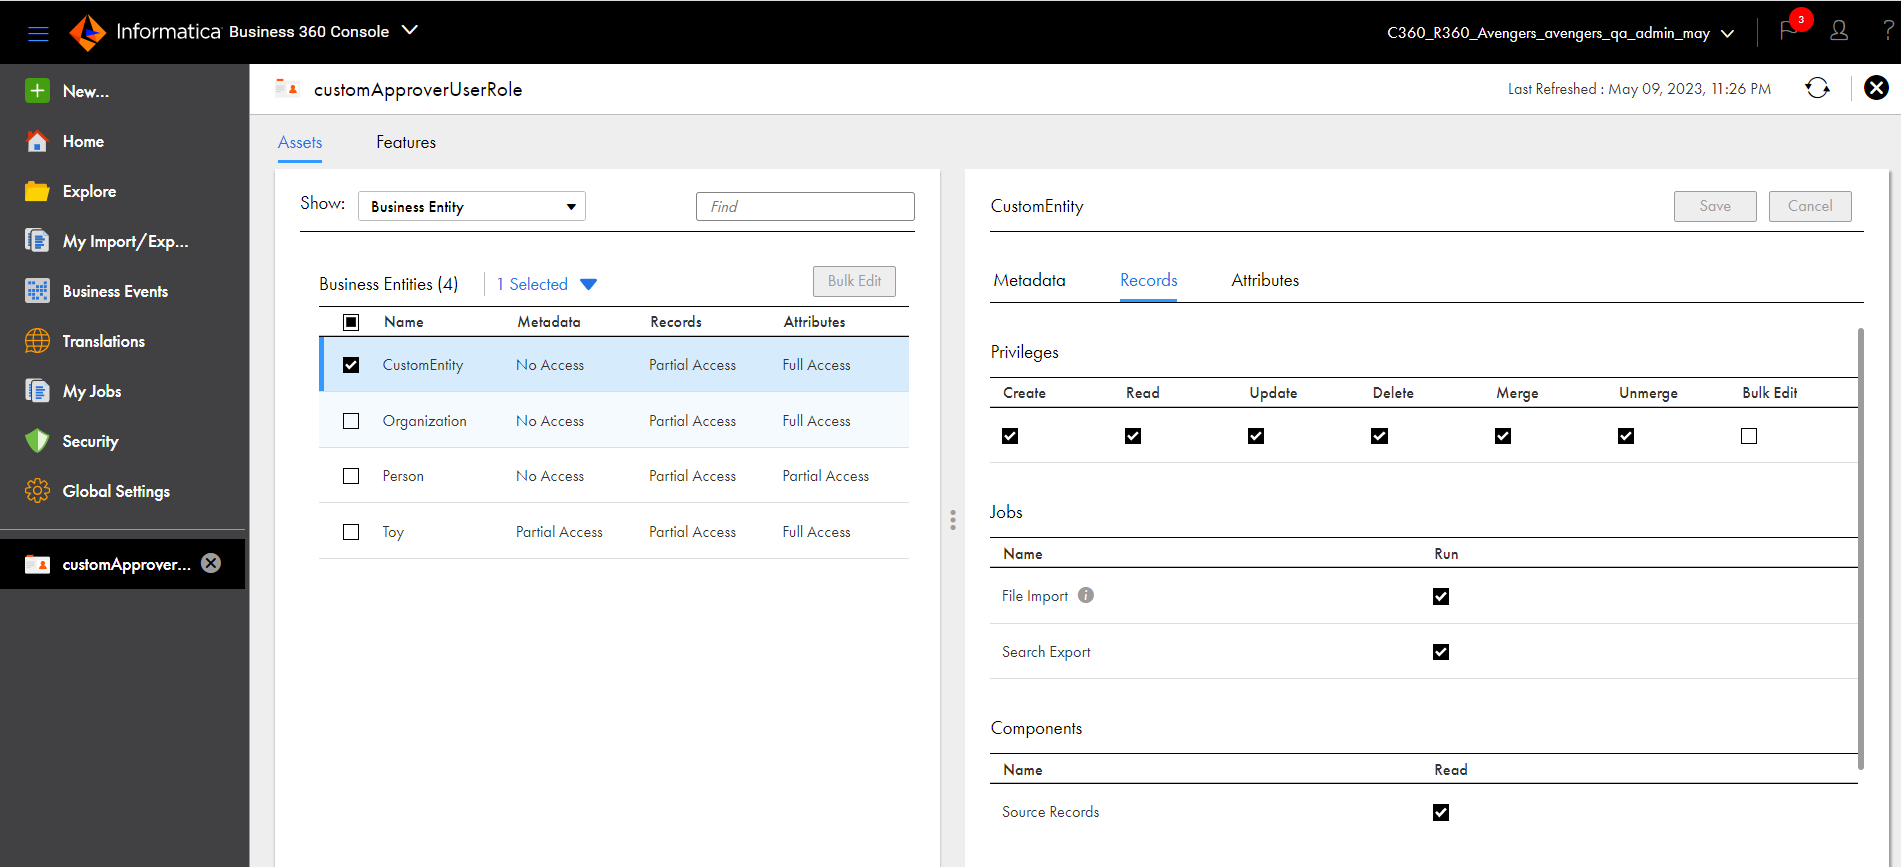
Bulk Edit
Edit business entity records in bulk.
Before you assign the bulk edit privilege, ensure that you assign the read and update privileges to the user role on the Records tab or the Attributes tab.
Note:
Users with Admin and Customer 360 Manager roles can also edit the records in bulk.
Note:
Effective in the May 2023 release, the option to assign the bulk edit privilege for custom user roles is available for preview.Preview functionality is supported for evaluation purposes but is unwarranted and is not supported in production environments or any environment that you plan to push to production. Informatica intends to include the preview functionality in an upcoming release for production use, but might choose not to in accordance with changing market or technical circumstances. For more information, contact Informatica Global Customer Support.
The privileges that you assign on the Records tab aren't automatically assigned to all fields on the Attributes tab. You can fine-tune the privilege for each field within the Attributes tab without dependance on the record-level privileges. For more information on assigning privileges for each field within a record, see Configure field privileges for business application user roles.
1On the Security page, open the user role for which you want to assign privileges pertaining to records in your business application.
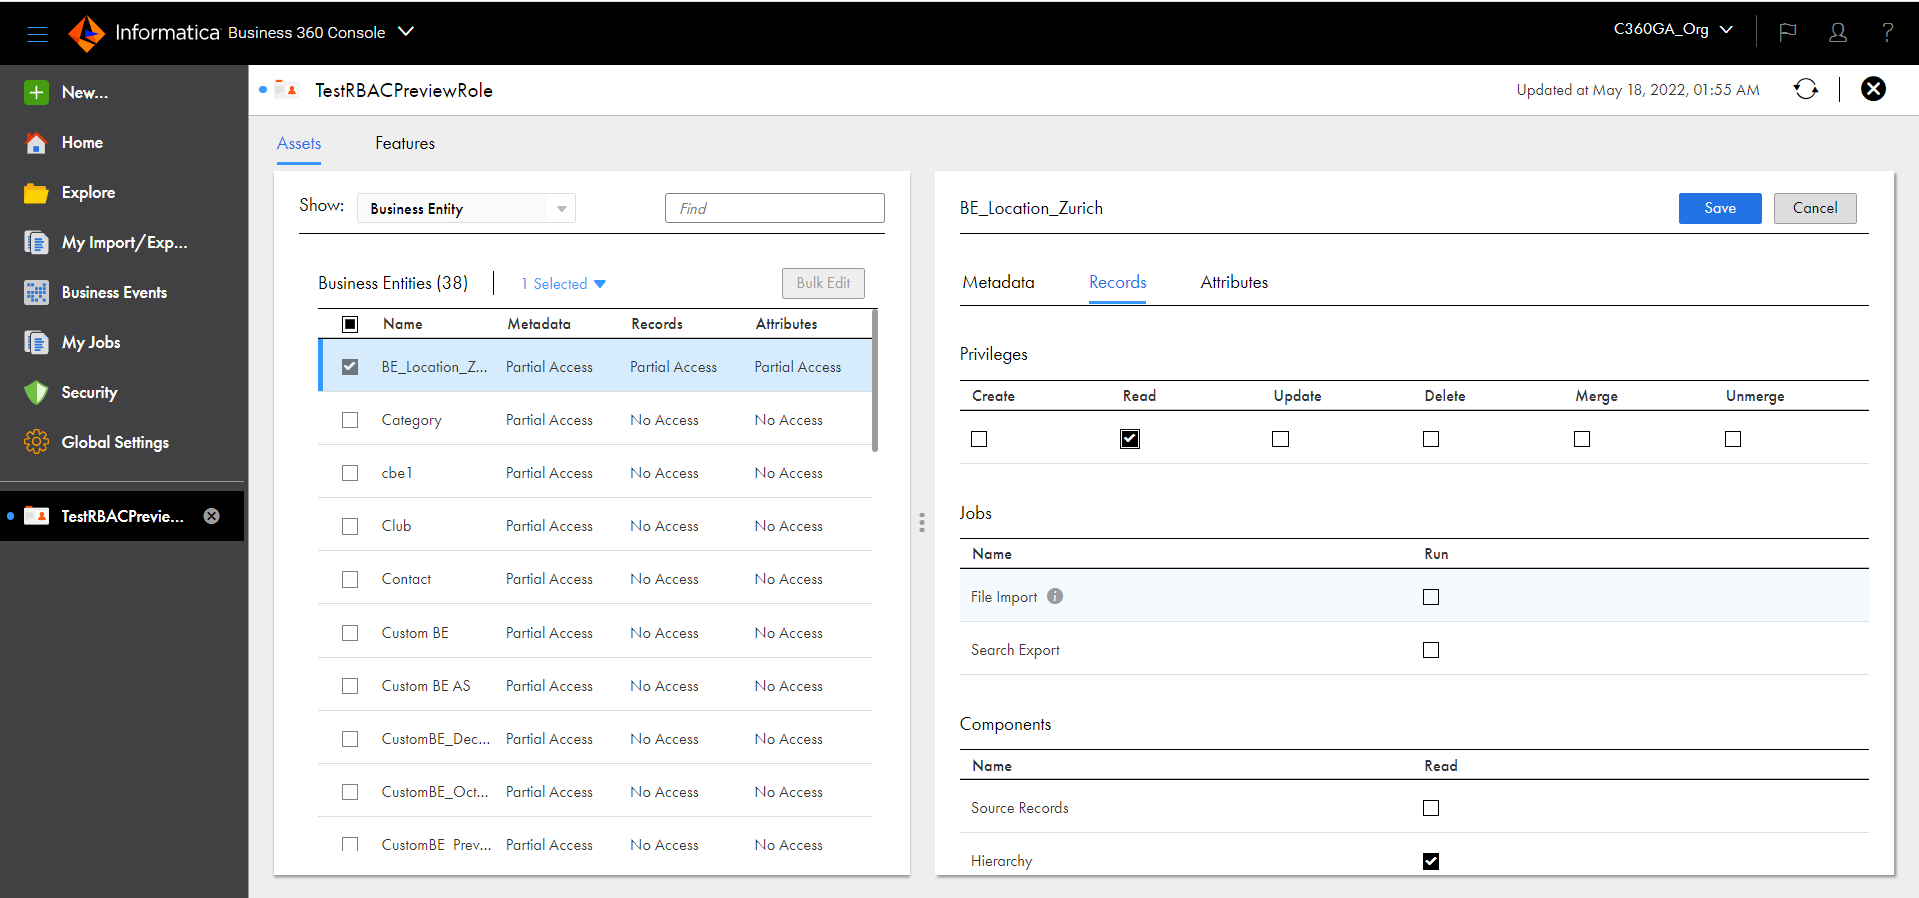
The user role details page appears. The following image shows the Records tab:
Note:
The Hierarchy check box in the Components section is not configurable in the current release.
2 Select the required privileges.
3Click Save.
Note:
To configure workflow privileges for the create, update, delete, and unmerge of records by a custom user role, follow the steps described in Configure workflow privileges for business application user roles.
File Import
You can specify whether a user with a custom user role can import all data without matching into MDM SaaS. To authorize a user to import all data into MDM SaaS, assign privileges in Administrator and on the Security page of Business 360 Console.
Note:
To access file import in MDM SaaS, ensure that you assign the Admin and Business360ProcessExecutor user roles.
1In Administrator, click User Roles.
The user roles page with a list of pre-defined and custom user roles appears.
2Select the custom user role for which you want to configure privileges.
The user role details page appears.
3Configure appropriate permissions for the Data Quality and MDM Business Application services.
For more information on these privileges, see Prerequisites.
4Click Save.
5Click Users.
The list of available users appears.
6Select the user for which you want to configure privileges.
The user details page appears:
7Assign a custom user role and the Business360ProcessExecutor role to enable a user to import all data without matching.
8Click Save.
9In Business 360 Console, click Security. Click the custom user role for which you want to assign privileges for importing data into your business application.
The user role details page appears.
10 Ensure that you select the required business entity for which you want to assign the privileges.
11On the Records tab, select Create and Update.
The create and update privileges are selected for all the fields on the Attributes tab.
12In the Jobs section, select Run for the file import job.
13Optionally, on the Attributes tab, modify the privileges for specific fields.
During import, the job excludes the fields for which the user doesn't have create and update privileges. These fields don't appear on the Map Fields page of the File Import wizard.
14Click Save.
Search Export
You can specify whether a user with custom user role can search for records in your business application and export all the records found using the search box or the filtered search option. You can also assign partial access for searching and exporting specific fields within a record.
1In Business 360 Console, click Security. Click the custom user role for which you want to assign privileges for executing search and export job in your business application.
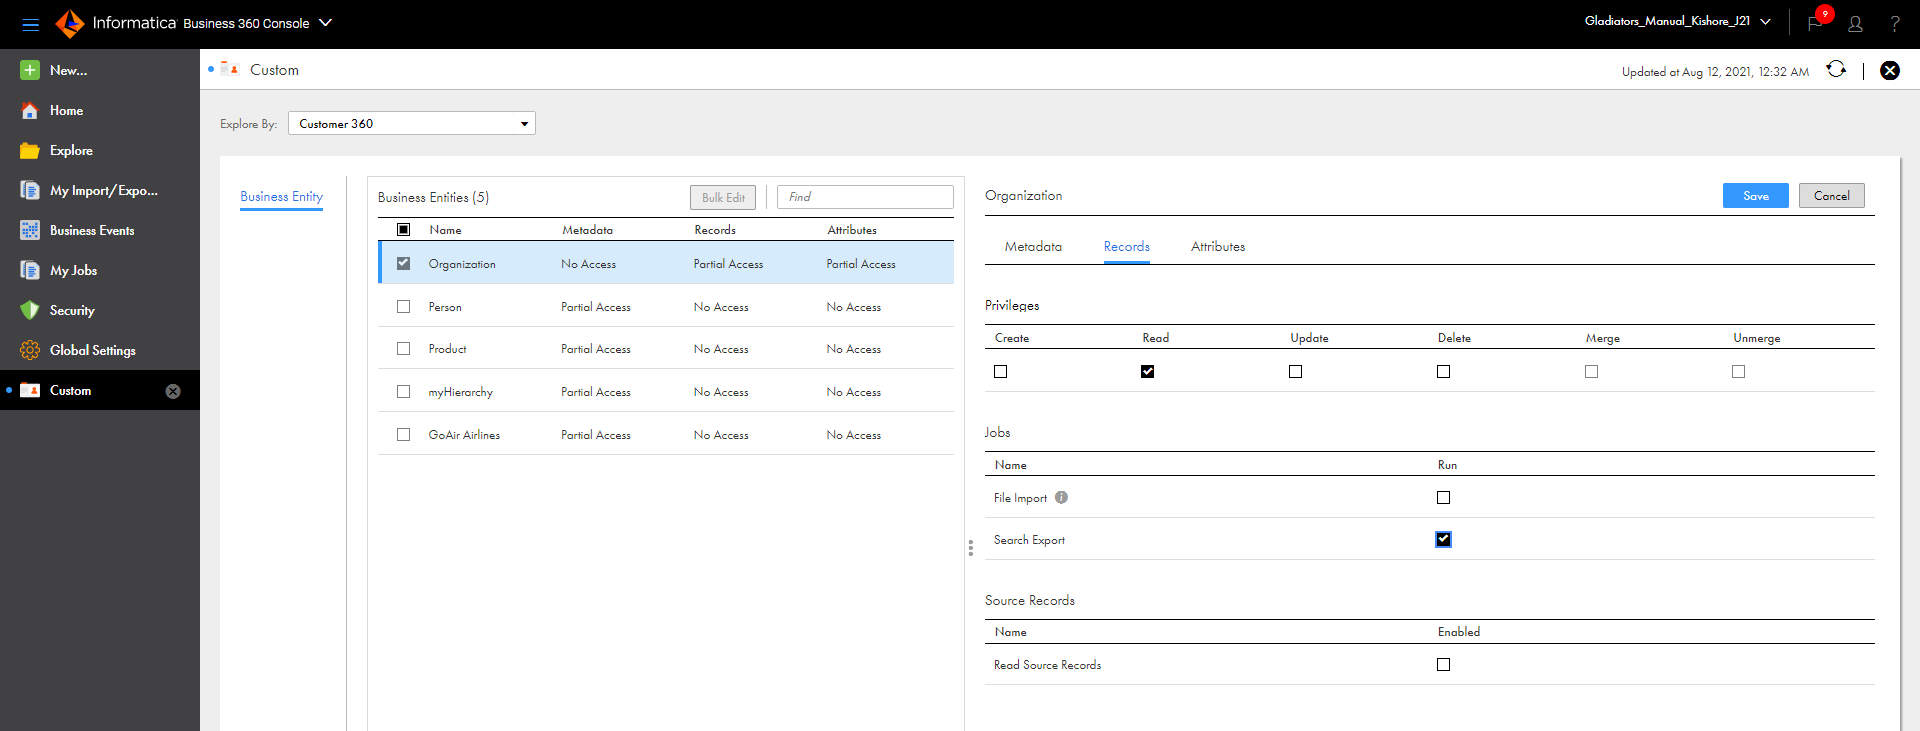
The user role details page appears. The following image shows the Records tab:
2 Ensure that you choose required business entity.
3On the Records tab, select Read in Privileges section and Run for Search Export job in Jobs section.
Without the read privilege for records, the user cannot search and view the records.
The read privilege is selected for all fields in the Attributes tab.
4Optionally, on the Attributes tab, modify read privileges for specific fields if required.
During export of search results, the job excludes the fields for which the user does not have read privilege.
5Click Save.
External match
You can specify whether a user with a custom user role can match external data with source or master records and then import or export data. To authorize a user to match external data with source or master records, assign privileges in Administrator and on the Security page of Business 360 Console.
1In Administrator, click User Roles.
The user roles page with a list of pre-defined and custom user roles appears.
2Select the custom user role for which you want to configure privileges.
The user role details page appears.
3Configure appropriate permissions for the Data Quality and MDM Business Application services.
For more information on these privileges, see Prerequisites.
4Click Save.
5Click Users.
The list of available users appears.
6Select the user for which you want to configure privileges.
The user details page appears.
7Assign the custom user role that you configured in 3 and the Business360ProcessExecutor role.
8Click Save.
9In Business 360 Console, click Security.
10Click the custom user role that you assigned to the user.
The user role details page appears.
11 Ensure that you select the required business entity for which you want to assign the privileges.
12On the Records tab, perform the following tasks:
aIf you want the user to match external data with master records and then export data, select Read.
bIf you want the user to match external data with source records and then import data, select Create and Update.
The read, create, and update privileges are selected for all the fields on the Attributes tab based on the privileges assigned to the user.
13In the Jobs section, select Run for external match.
14Optionally, on the Attributes tab, modify the privileges for specific fields.
Source Records
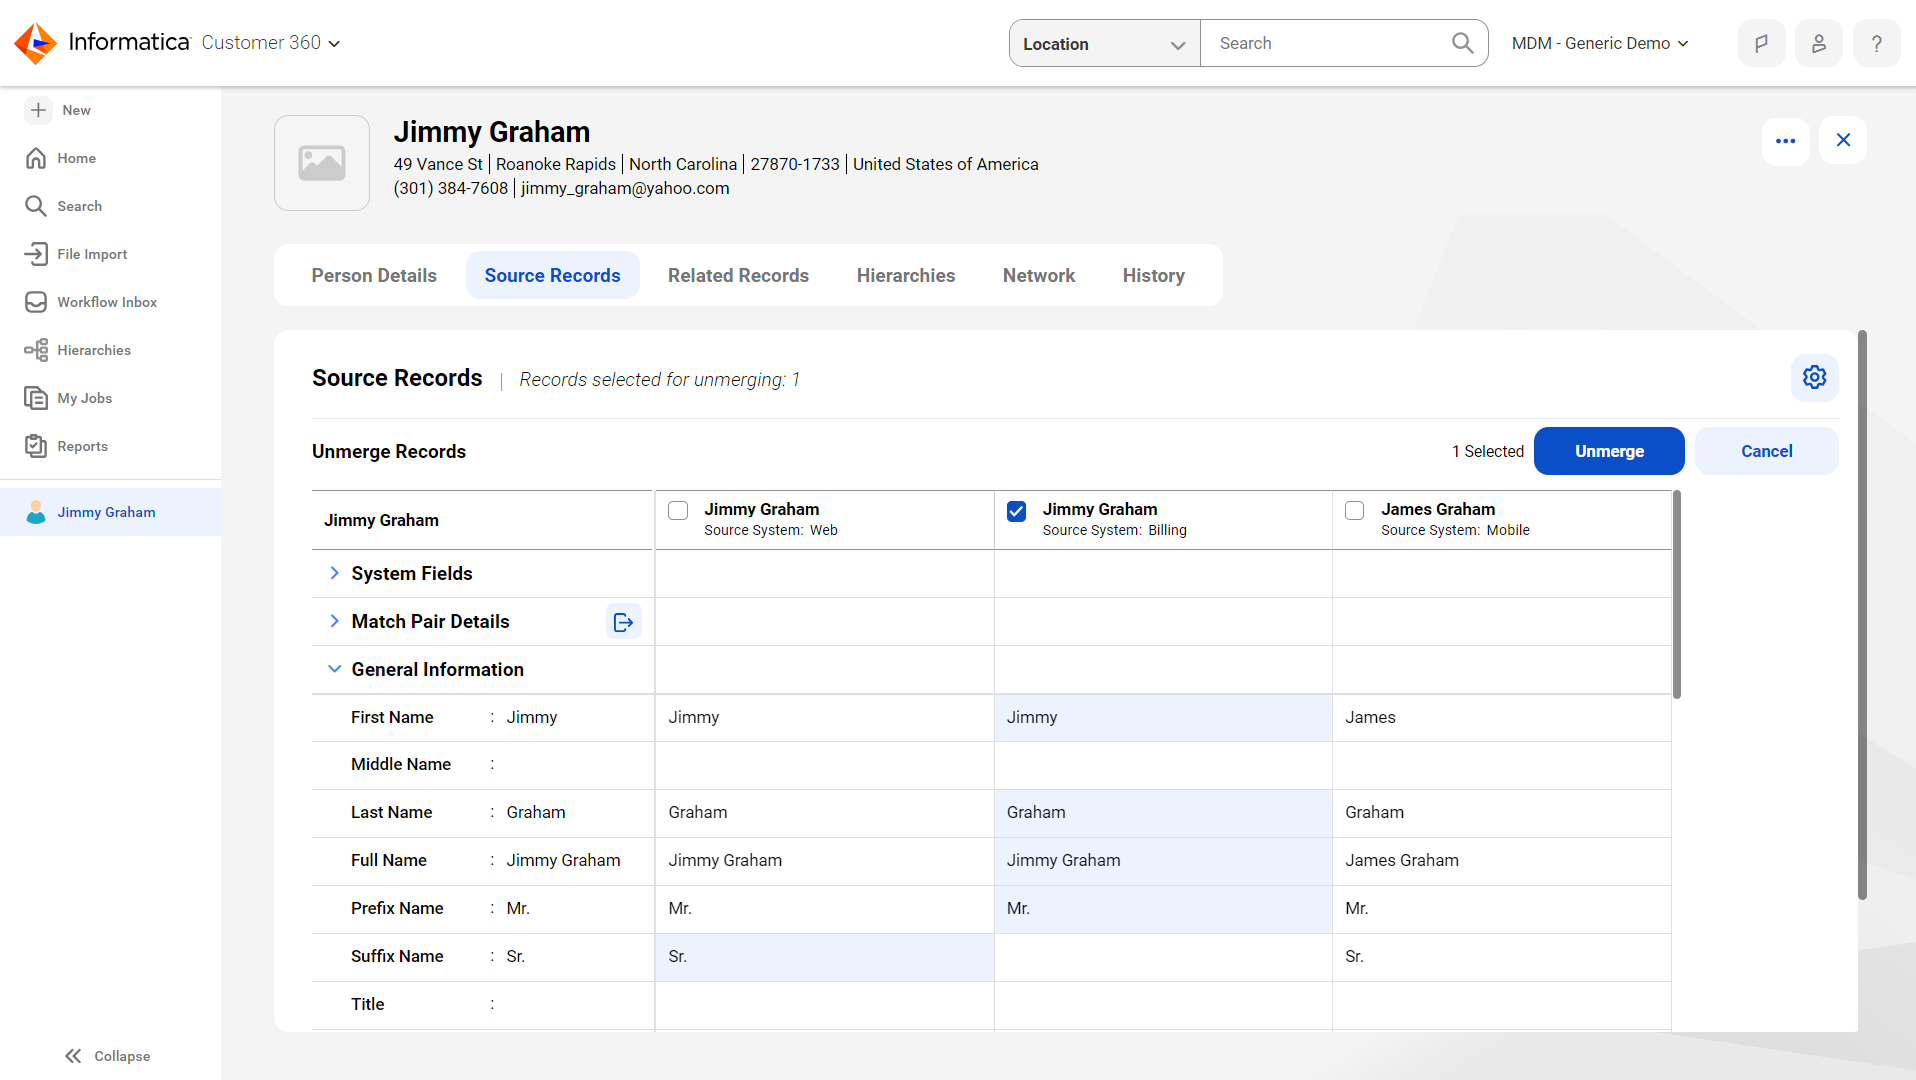
The privilege specifies whether users get the source records details when they open a record. The users must also have the read privilege for records to view the source records.
When the user searches for a record within your business application, the Source Records tab is not visible if you do not assign read privilege for source records. If you do not assign the read privilege, the Source Records tab is hidden for all records pertaining to the selected business entity.
The following image shows the Source Record tab of a record:
If you fine-tune the privileges for each field within a record on the Attributes tab, the Source Records tab will exclude the fields for which the user does not have read privilege.
Hierarchy
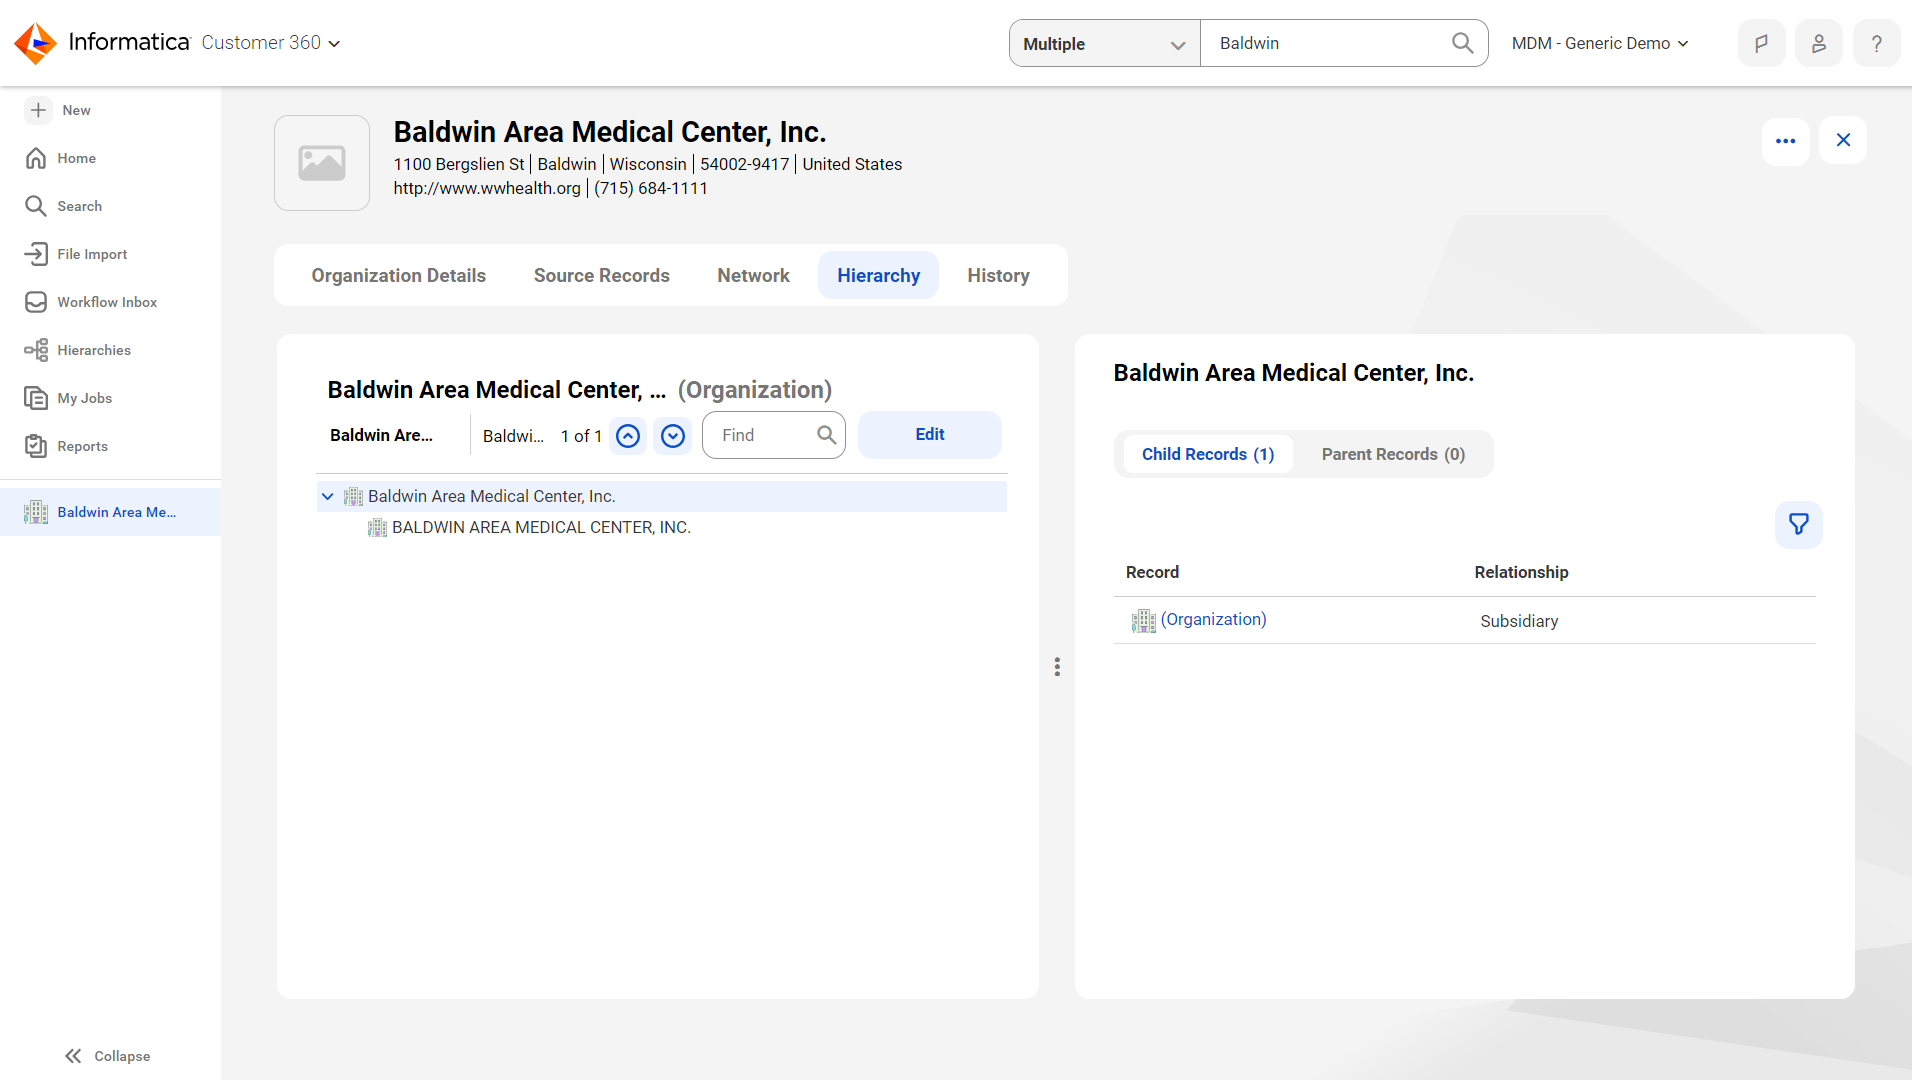
The privilege specifies whether users get the hierarchy details when they open a record.
When the user searches for a record within your business application, the Hierarchy tab is not visible if you do not assign read privilege for the hierarchy component. If you do not assign the read privilege, the Hierarchy tab is hidden for all records pertaining to the selected business entity.
Note:
By default, the Hierarchy tab is visible only for the predefined user roles, such as Admin, Customer 360 Analyst, Customer 360 Data Steward, Product 360 Manager, and Supplier 360 Data Steward.
To enable the Hierarchy tab for the other predefined user roles, you can create a custom user role with read-only privilege for the Hierarchy Component and assign the custom user role to users.
The following image shows the read privilege selected for the Hierarchy component in the Records tab of the selected business entity:
The following image shows the Hierarchy tab of a record:
Note:
The hierarchy details that the user can view on the Hierarchy tab is based on the privileges that you assign for the hierarchy. For more information on hierarchy privileges, see Configure hierarchy privileges for business application users.
Match Analysis and Explainability Dashboard
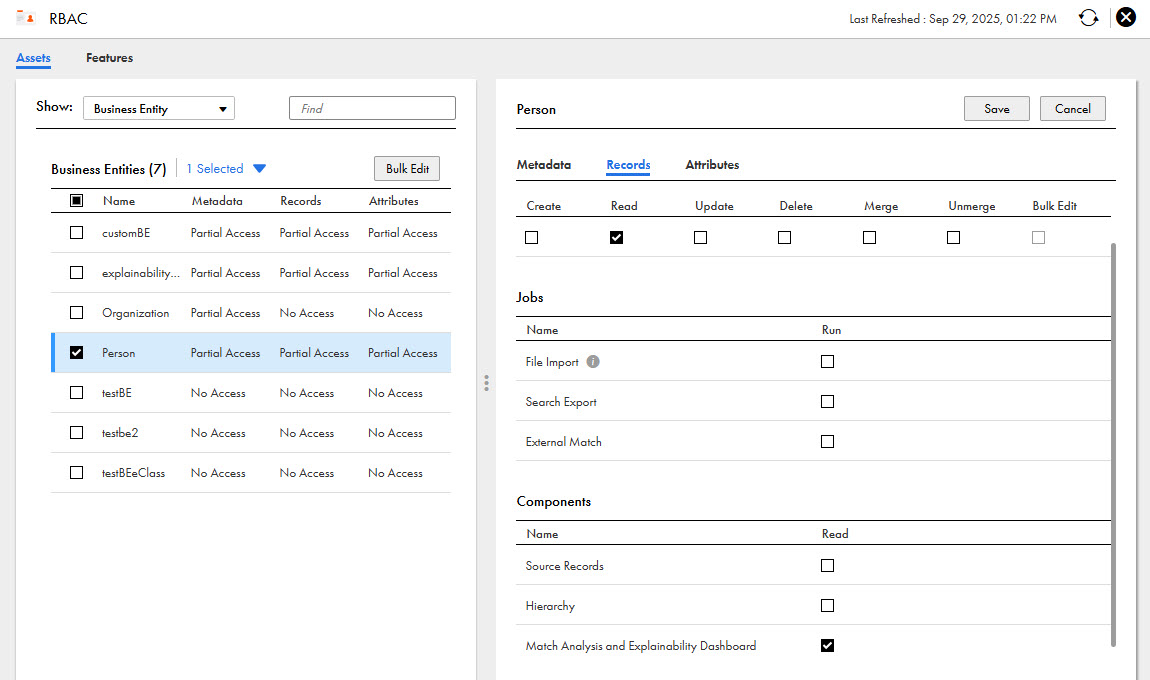
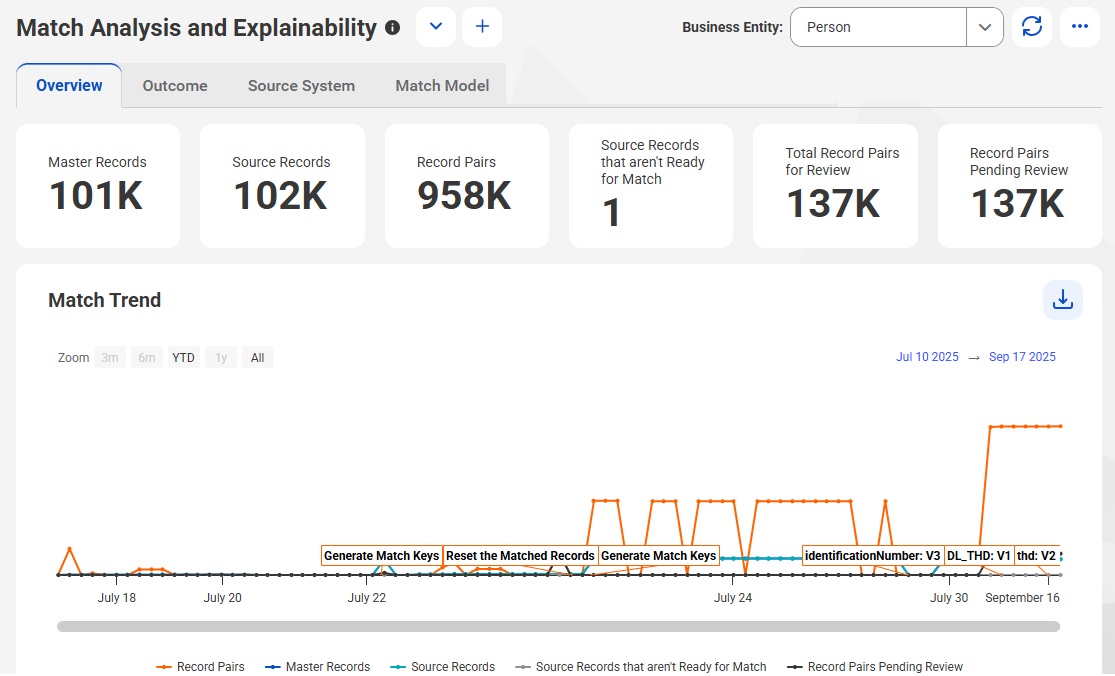
The privilege specifies whether users with custom user roles can access data on the Match Analysis and Explainability dashboard related to a specific business entity.
To allow users with custom user roles to access data on the dashboard, ensure that you assign the following privileges:
•Assign the Match Analysis and Explainability Dashboard privilege on the Security page.
•Assign read privileges for the records and attributes related to the selected business entity.
Users assigned to a customer user role without these privileges can't view any metrics related to match analysis and explainability for the selected business entity.
Note:
By default, users with Admin user role can access data on the Match Analysis and Explainability dashboard.
The following image shows the read permission assigned for accessing the Match Analysis and Explainability Dashboard related to the Person business entity:
The following image shows the Match Analysis and Explainability dashboard: