Configure related records privileges for business application users
You can configure privileges that specify whether users can create, read, update, and delete related records within a record. You can also specify whether users can import relationship data.
Related Records
You can configure privileges that specify whether users can create, read, update, and delete related records within a record in your business application.
The following table describes the behaviour of related record privileges:
Privileges
Set to Enabled
Create
Add related records to a record. When a user with custom user role adds related records, the user can view only those relationships for which you have assigned the create privilege. If the user does not have the create privilege for any of the relationships, then the user cannot view the Related Records section in the record details page.
Read
View the relationship in the related records section of a record and the Relationship Graphs tab of a record.
Update
Update the related records of a record.
Delete
Delete related records of a record. If you do not assign this privilege for a relationship, the delete icon adjacent to the related record does not appear in the related records section.
1On the Security page, open the user role for which you want to assign privileges pertaining to related records in your business application.
The user role details page appears.
2Select Relationship.
The list of predefined and custom relationships appear.
3Select the required relationship for which you want to assign related records privileges for the custom user role.
4On the Records tab, select the required privileges.
Note:
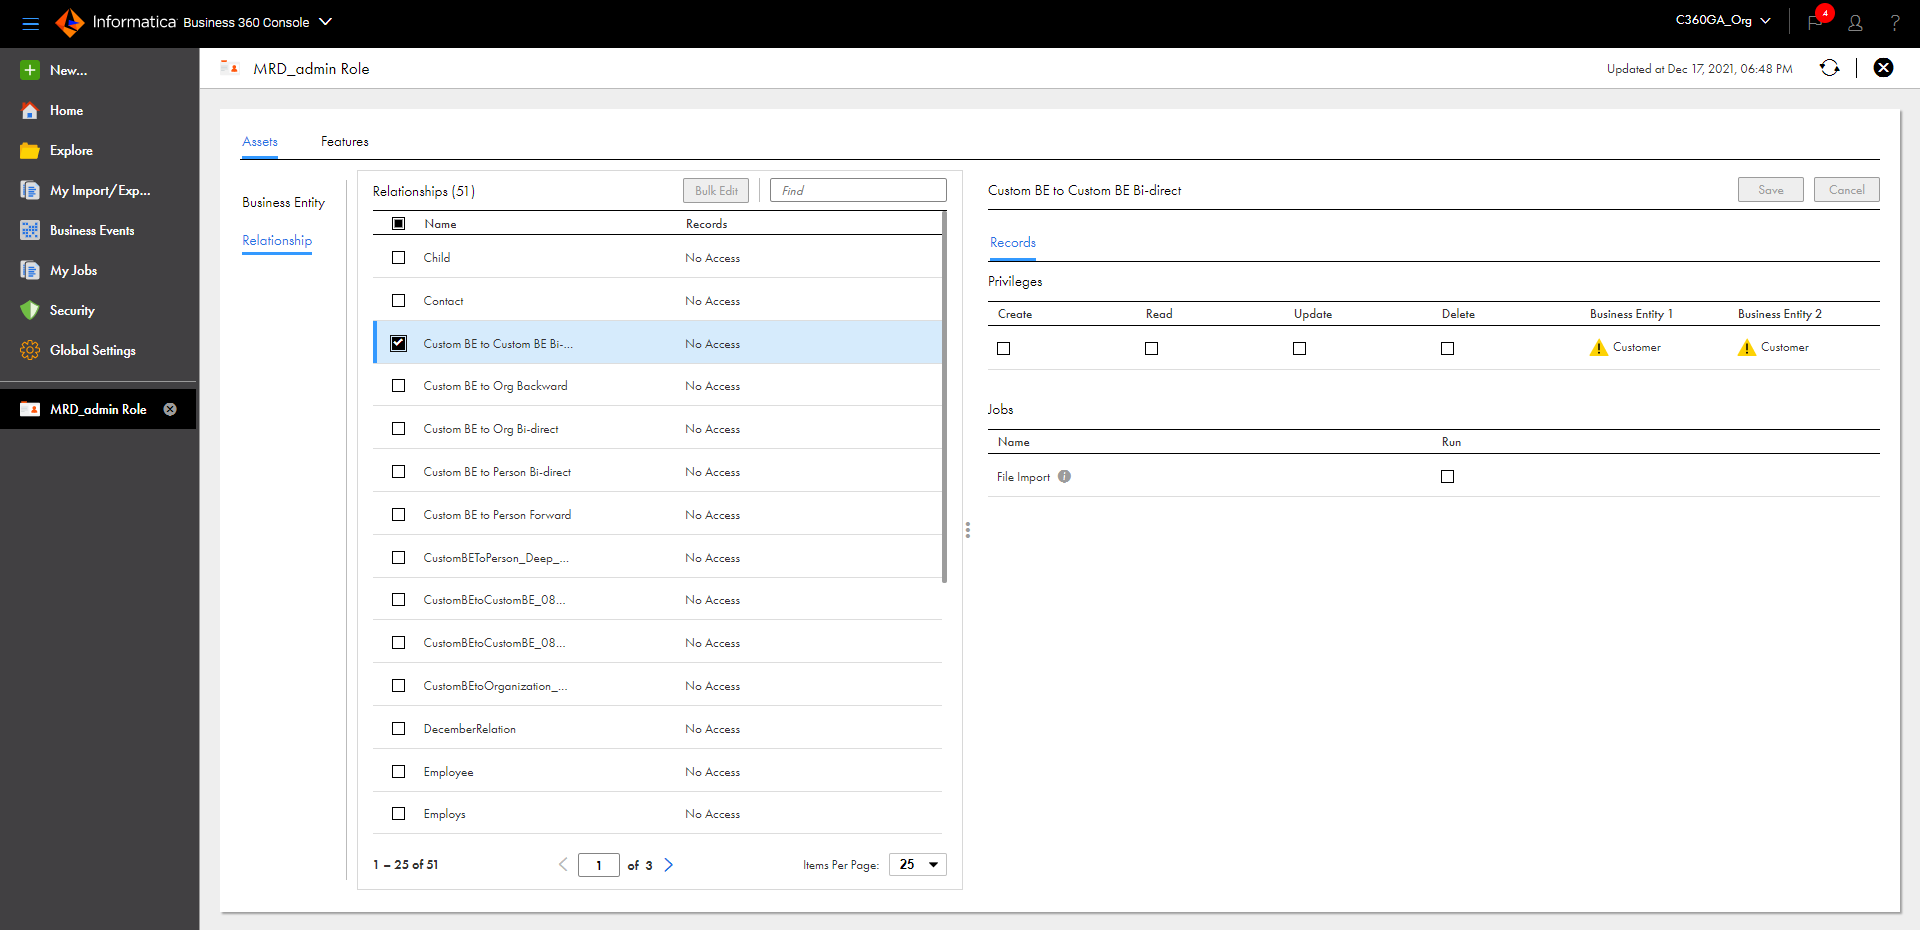
On the Records tab, you can also view the business entities associated with the selected relationship. You must assign read privilege for the business entities associated with the relationship. You can view a warning message adjacent to the business entity if you have not assigned the read privilege.
The following image shows the shows the details of a relationship with a warning icon indicating that the user role does not have read privilege for the business entity:
5Click Save.
File Import
You can specify whether a user with custom user role can import relationship data into your business application. To authorize a user to import relationship data into your business applications, you need to assign privileges in Administrator and on the Security page of Business 360 Console.
1In Administrator, click Users.
The list of available users appears.
2Select the user for which you want to configure privileges.
The user details page appears:
3Assign a custom user role and the Business360ProcessExecutor role to enable a user to import data.
4Click Save.
5Click User Roles.
The user roles page with list of pre-defined and custom user roles appears.
6Select the custom user role for which you want to configure privileges.
The user role details page appears.
7Configure appropriate permissions for the MDM Business Application service.
For more information on the privileges of the MDM Business Application service, see Prerequisites.
8Click Save.
9In Business 360 Console, click Security and click the custom user role for which you want to assign privileges for importing relationship data.
The user role details page appears.
10On the Relationship tab, ensure that you select the required relationship for which you want to assign the privileges.
11On the Records tab, select Create and Update.
12In the Jobs section, select Run for the file import job.
13Click Save.
The relationships for which you assign the privileges for file import appear in the Target Relationship section when the user with custom user role imports relationship data in your business application.